2014, the year that infosec gets political
2013 has certainly been a watershed year for information security. But to understand how things might subsequently unfold in 2014, it's worth remembering that each and every revelation of 2013 will be processed and acted upon by humans. Humans with…
Jan 06 14January 06, 2014
Article at CSO Online Australia
Turn your security inside out for added agility, says Oracle
"What we see is organisations fundamentally failing in their security because what they're trying to do is to hold the wall, and the wall doesn't exist any more. We've moved stuff out into the cloud, we've moved stuff out into tablets and put it out…
Dec 20 13December 20, 2013
Article at CSO Online Australia
To prevent phishing, punch your employees in the face
"How do you teach a person to duck a punch? You punch them in the face until they get it," said freelance information security consultant Dan Tentler, who designed Twitter's internal anti-phishing training program, at last week's…
Nov 01 13November 01, 2013
Article at CSO Online Australia
Upping the pace to face the infosec 'Cold War'
2013 has become the year of cyber-espionage we were warned about. This online 'Cold War' demands a faster pace and a proper analytical basis, says Tenable Network Security"We, as far as I'm concerned, are in an arms race. It's the same…
Oct 01 13October 01, 2013
Article at CSO Online Australia
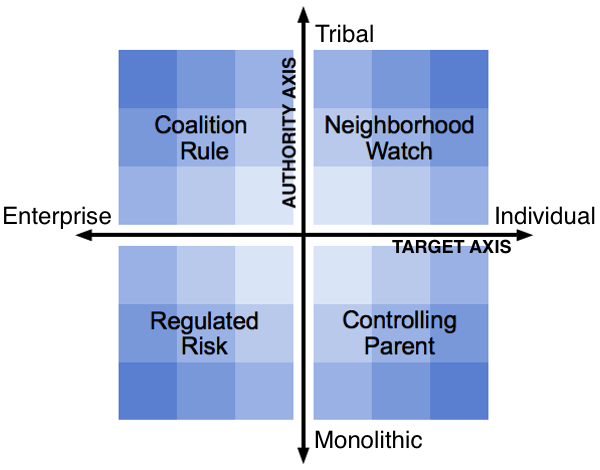
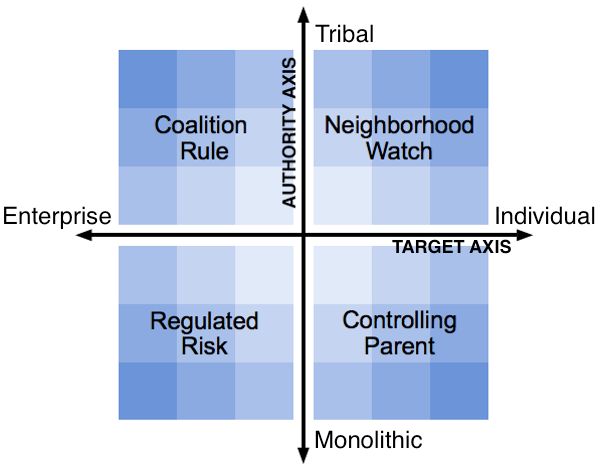
Gartner's vision of infosec 2019: four scenarios, all bad
Will it be the total surveillance society and internet licenses? A breakdown of authority, with e-militias fighting extreme anarcho-hactivists? Or one of the other two?Global research and advisory firms are meant to give you the big picture. That's…
Aug 28 13August 28, 2013
Article at CSO Online Australia
The 10 Commandments of Data Sovereignty
The Cyberspace Law and Policy Centre at the University of New South Wales' Faculty of Law yesterday launched the whitepaper Data Sovereignty and the Cloud: A Board and Executive Officer's Guide, an easy-to-read document intended to help…
Jul 04 13July 04, 2013
Article at CSO Online Australia
UNSW helps close cloud computing's can of (legal) worms
How does your organisation cope when your data has left the building — or the country? Data sovereignty can be a vital legal issue, because data becomes subject to the laws of the country it's stored in — and that changes the risk…
Jul 04 13July 04, 2013
Article at CSO Online Australia
Schneier joins EFF board in wake of NSA scandal
Renown cryptologist and security specialist Bruce Schneier has joined the board of the Electronic Frontier Foundation (EFF), one of the United States' longest-running and most influential digital rights and civil liberties lobby groups.…
Jun 29 13June 29, 2013
Article at CSO Online Australia
Australia's Privacy Commissioner gets serious about infosec
According to Australia's Privacy Commissioner, Timothy Pilgrim, every single one of the high-profile investigations he completed in 2011–12 involved data security issues and information security is now the major issue affecting consumer…
May 01 13May 01, 2013
Article at CSO Online Australia
Verizon DBIR confirms we're rubbish, so let's do something about it
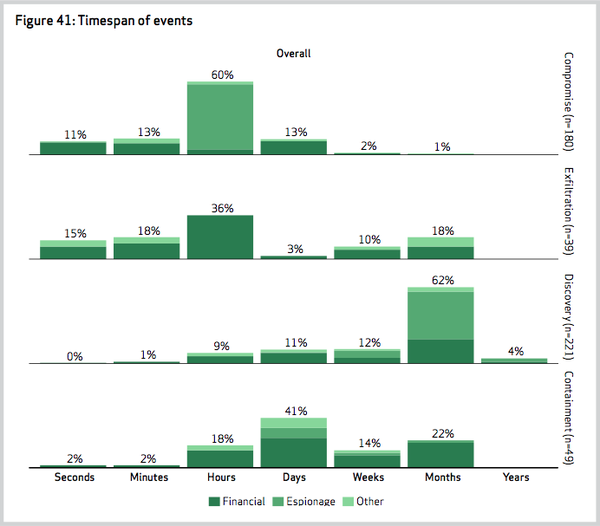
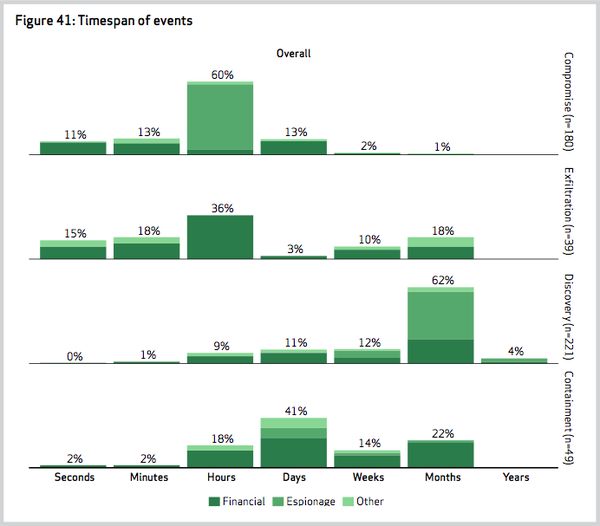
Verizon's latest Data Breach Investigation Report (DBIR) provides its usual comprehensive and witty overview of our infosec war against the bad guys. But we already know its core messages, or should do: we're rubbish at defending ourselves, we're not…
Apr 23 13April 23, 2013
Article at CSO Online Australia
Trend Micro's new paradigm: old (but good) advice in a new bottle
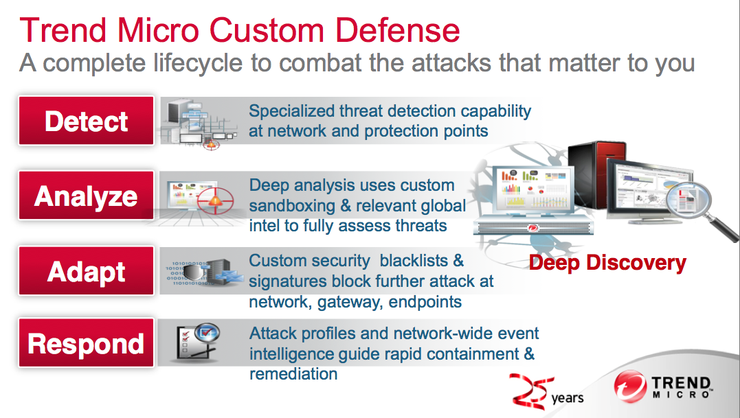
Information security vendors are telling customers to think in a new way. At the core of their advice is the idea — the admission, if you like — that no matter how good the defences they sell, sooner or later the bad guys will get through.Trend…
Apr 01 13April 01, 2013
Article at CSO Online Australia
Microsoft's Melbourne tests confirm: counterfeit software a security risk
A test of counterfeit Microsoft Windows and Office installers bought from local markets in Melbourne, Australia, seems to confirm the results of recent IDC research: dodgy software is generally either rubbish or a security…
Mar 28 13March 28, 2013
Article at CSO Online Australia
Vulnerability mythbuster: Windows, Flash good; Apple, Linux bad
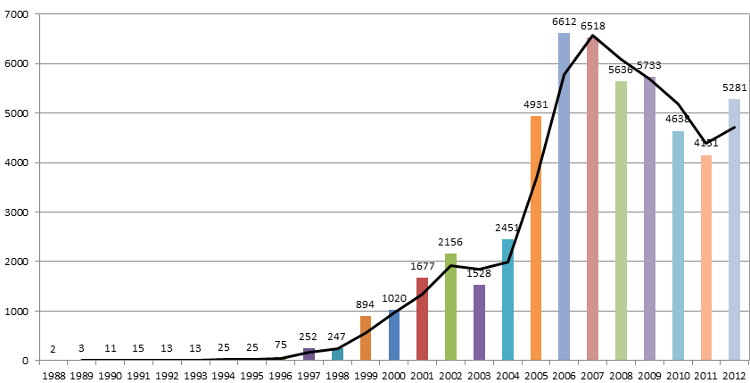
Have we beaten the hackers, at least on one front? The number of discovered and reported software vulnerabilities increased rapidly from 1988 to 2005, peaked in 2006, then started dropping. But they rose again in 2012. A glitch in a real decline? Or…
Feb 26 13February 26, 2013
Article at CSO Online Australia
Chinese attacks show up useless infosec, again
Recent attacks on US newspapers are further proof that, despite making billions, the information security industry is pretty much screwed.My American colleague Antone Gonsalves has written up some lessons learned from the…
Feb 05 13February 05, 2013
Article at CSO Online Australia
Nasty Ruby on Rails vulnerabilities highlight small websites' risk to us all
The revelation of serious long-term vulnerabilities in the popular Ruby on Rails web programming framework is just one of three events in the last 72 hours that have convinced me that improvement in web application security is…
Jan 11 13January 11, 2013
Article at CSO Online Australia
Could 2013 be the year we finally sort out security?
In a recent episode of a certain podcast, we discussed the idea that the new mobile platforms represent a once-in-a-generation opportunity to transform online security. Whichever platform you pick -- iOS, Android or Windows Phone -- it's potentially…
Dec 24 12December 24, 2012
Article at CSO Online Australia
2012: the Year of Cyberwar that wasn't
It was going to be the year of cyberwar, we were told on the eve of 2012. We've seen plenty of scary news stories since about dangerous nation-state actors, usually without naming them. But I reckon we've now got the focus wrong.That's…
Dec 22 12December 22, 2012
Article at CSO Online Australia
Cyber crime wave: tsunami or ripple?
A new cybercrime survey by Australian outfit Essential Research has begun to unravel the threads that vendors tend to tangle. Their initial results suggest things might not be nearly as bad as we're told.When it comes to inflated online…
Nov 03 12November 03, 2012
Article at CSO Online Australia
High praise for Oz DSD's "Catch, Patch, Match"
The newly-updated Top 35 Mitigation Strategies from Australia's Defence Signals Directorate (DSD) has received high praise from Alan Paller, founder and director of research of the SANS Institute. It could even make Australia the…
Oct 27 12October 27, 2012
Article at CSO Online Australia
DSD confirms: application whitelisting is the go
Australia's Defence Signals Directorate (DSD) has joined the increasing number of organisations promoting application whitelisting as a key security strategy with an updated version of its award-winning "Top 35 Mitigation…
Oct 25 12October 25, 2012
Article at CSO Online Australia