The cryptocurrency industry is scrambling to confront a fast-moving threat with outdated defenses. Artificial intelligence (AI) gives crypto scammers a powerful new playbook – and investors are paying the price.
In traditional finance (TradFi), banks can freeze accounts and reverse fraudulent transactions, but in crypto, a single phishing site or fake “support bot” can empty a wallet instantly, with no recourse.
Crypto’s biggest weakness isn’t market volatility; it’s trust, and scams are eroding it faster than price swings. Static defenses and post-mortem reports are backward-looking, yet the industry remains reactive. By the time breaches are reported or reimbursed, funds are already gone.
At Token2049, Alex Katz, CEO of Web3 security firm Kerberus, sounded the alarm: self-custody alone is not enough – users need dynamic safeguards at the wallet and transaction layer.
Techopedia sat down with Katz to talk about why real-time protection at the transaction level is essential as the next security benchmark to preserve trust and prevent losses before they happen.
- Traditional defenses like audits, bug bounties, and blacklists are too static to keep up with fast-evolving crypto scams.
- Crypto is still the Wild West – there are not enough security measures and standardized processes for audits and other defenses to be effective.
- Real-time, AI-driven protection at the wallet and transaction layer is critical to preserving trust in Web3.
- Effective protection should run in the background so that users aren’t even aware of it, it simply works.
- Crypto holders should use a hardware wallet to avoid losing their coins and tokens to malware that steals their seed phrases or private keys.
Alex Katz is CEO & Co-Founder of Kerberus. Alex brings operational discipline from his years directing global marketing initiatives and scaling international teams. His background in financial markets and digital growth informs Kerberus’ strategic development, ensuring their security solutions meet enterprise standards while remaining accessible to individual users.
AI-Enhanced Scams & Crypto’s Inadequate Defenses
Q: How are criminals weaponizing AI in crypto scams, and what makes them different from older phishing or social engineering attacks?
A: AI improves criminals as much as it improves security companies. The biggest vector where AI is likely to continue improving as a technology is in pig butchering scams, where people are deceived into doing something because they are led to believe they are speaking with someone.
With advancements in video technology and the increasing quality of videos, it will become even more challenging than before, especially for older individuals. However, even for younger people, it will be tough to know. We’ll need to establish some form of human agreement between people so that we know how to identify each other. It continues to worsen, and it’s something that education can truly help alleviate.
But we are against education for phishing. In crypto, there’s the very well-known phrase “do your own research.” There are risks of buying a low-quality token versus a high-quality token. That makes sense, but “do your own research” is thrown around as in, “you must make sure that you don’t make any mistakes whatsoever, or you can lose everything.” That’s the current state of crypto.
We believe that you will reach 10% of the user base by educating them. It’s good, it’s necessary, but what we create are these automated security solutions where the user doesn’t need to be educated. They just need to use our technology, and then they are protected from losing funds, both because the technology is so good and also because we offer coverage up to $30,000 if the technology fails.
Q: Why is it the case that audits and security defenses aren’t working?
A: Crypto doesn’t have standard procedures for smart contracts whatsoever. First of all, contracts can be upgraded, meaning that whatever was audited for a contract can completely change in the next iteration of the contract, and if you didn’t spend that crazy amount of money to safeguard it again with the audits, then you’re exposed to criminals.
That also leads to the auditing companies having a bad reputation – “they audited it, but it got hacked.” No, they audited the version that didn’t get hacked, but then got upgraded.
In traditional computer systems and business, we have ISO processes and certifications that require contracts to be completed in a certain way. And if there is an upgrade, you must follow certain steps.
We would have different results, but we are still in the Wild West of crypto. Everyone creates whatever they want, iterates however they want, and upgrades however they want. There are not enough security measures, and that’s why it fails. We need more standardized processes.
Why Reactive Security No Longer Works in Crypto
Q: What are the risks of staying in reactive mode rather than being proactive?
A: It is impossible to take a reactive approach in crypto because, for example, in credit cards, if you swipe your card and someone steals it, you call your bank or your credit card issuer and tell them the card was skimmed or stolen. They charge back the transaction, which means you get your money back, and then they issue you a new card, sometimes at no cost, or sometimes you pay a small shipping fee; problem solved.
You don’t have that in crypto. And even if there are people who can help with recovery, recovery doesn’t start until anywhere between $100,000 and $300,000 in losses. So, anyone who lost below $100,000 has no recourse. If you lost your funds, you lost them. So that’s why we have to be proactive.
I don’t think we are reactive; it’s just that we are not doing the standard processes that we need in crypto, starting from knowing who you are investing with.
There are so many companies and projects that start in stealth mode. And then if it goes wrong, they say, “Okay, it was stealth, nothing happened.” However, if it goes right, they are happy to claim they’re the founder, CEO, CTO, and so on. We have to mature. We’re still too young.
Protecting Users Without the Tech Headaches
Q: What safeguards can be built directly into wallets to protect everyday users without requiring technical knowledge?
A: If I have to explain to you the safeguards, it’s already wrong. Every safeguard must be fully automated, and the user should not even notice its presence until an issue arises.
We protect Web3 sites that are designed to interact with non-custodial wallets, such as MetaMask, Phantom, and Rabby. If any website is designed or hacked to steal from them, we detect it automatically with 99.9% accuracy, and we warn them about it. They still have the option to choose; they can disregard our warning if they wish, at their own risk.
Another safeguard that we have is against address poisoning. If a user copies an address that is similar to one they have previously interacted with, we also display a warning. This is a security layer that we created nearly two years ago, which wallets still haven’t adopted, even though they could. It’s not a very hard engine to prevent; it’s a standard attack.
But unfortunately, wallets don’t have security at the top of mind for users. We hope to change that by partnering with wallets in the region.
The Shortage of Security Talent in the Crypto Industry
Q: Why don’t they have this focus on security, given the amount of money held in crypto?
A: We don’t have enough capable people working in security, anywhere in crypto, and especially today, with the rise of AI. For example, we just acquired a company, a competitor of ours, and the reason they were selling is that they wanted to work on AI.
So, the real talent is not working in crypto, and that has to do a lot with the nature of crypto, how volatile it is, how unsafe it is in every aspect.
That’s the main reason, and a lot of the security around wallets is built with the wrong approach. Because crypto is largely about transparency and open source, you can see the blockchain. However, companies are publicizing how they detect scammers, as that’s what they are pressured to do. And when you say how to detect the scammer, you’re just giving the key to the scammer to go around you.
From day one, we have never said how we do what we do for that reason. And it’s taken years for this to improve.
The Missing Piece: Prosecution & Accountability
Q: How do you see the role of regulators and the frameworks that should exist?
A: Regulation has improved a lot lately in the US. But prosecution is what’s missing. We have project founders who are rugging people, and they are not getting prosecuted whatsoever.
Some of them are well-known founders of today’s larger projects, but they face no repercussions for their past actions.
We also have bad actors across the board – from small players who create crypto drainers and are never caught, to major figures like Hayden Davis, who profited from projects such as Libra, possibly Melania, and now the Kanye coin. Despite repeating the same tactics, they still face no consequences. Some even appear on YouTube openly discussing their actions. To truly deter this behavior, we need stronger and more consistent prosecution in the crypto space.
How Everyday Users Can Protect Their Assets
Q: What’s your advice for the average user to keep their assets safe?
A: First and foremost, they need to use a hardware wallet, because the biggest attack right now is people downloading malware onto their devices that steals their seed phrases or private keys.
Once that happens, they’ve lost everything, but they’ve also lost ownership of the wallet, meaning that they have to scrap it and do something else completely. Sometimes, these individuals have future air drops to claim or staked tokens or NFTs, and they must hire a white-hat hacker to counter the hacker and retrieve them.
Just getting a $50 to $100 hardware wallet solves that issue. That’s all users need to do. It is inconvenient; you need to have a physical device with you and press buttons. I’m not saying it’s perfect, but it is 100% necessary.
And then they might consider installing our software. Sentinel 3 protects them on all EVM chains and Solana (SOL), boasting a 99.9% detection rate. It features multiple security rails, including address poisoning protection, and offers up to $30,000 of coverage in case of a missed issue, effectively covering their portfolio.
Q: What does real-time protection look like to the user?
A: Once they’re attempting the transaction, if it’s safe, they shouldn’t see anything, minus a small delay or wait. They should just proceed as normal.
If something is detected, they will be warned that they are about to lose their funds. That’s exactly what we do, and that’s what a bank does. If you attempt to wire funds from your bank account to an known bank account that has been flagged, the transaction will be stopped. It’s the same thing.

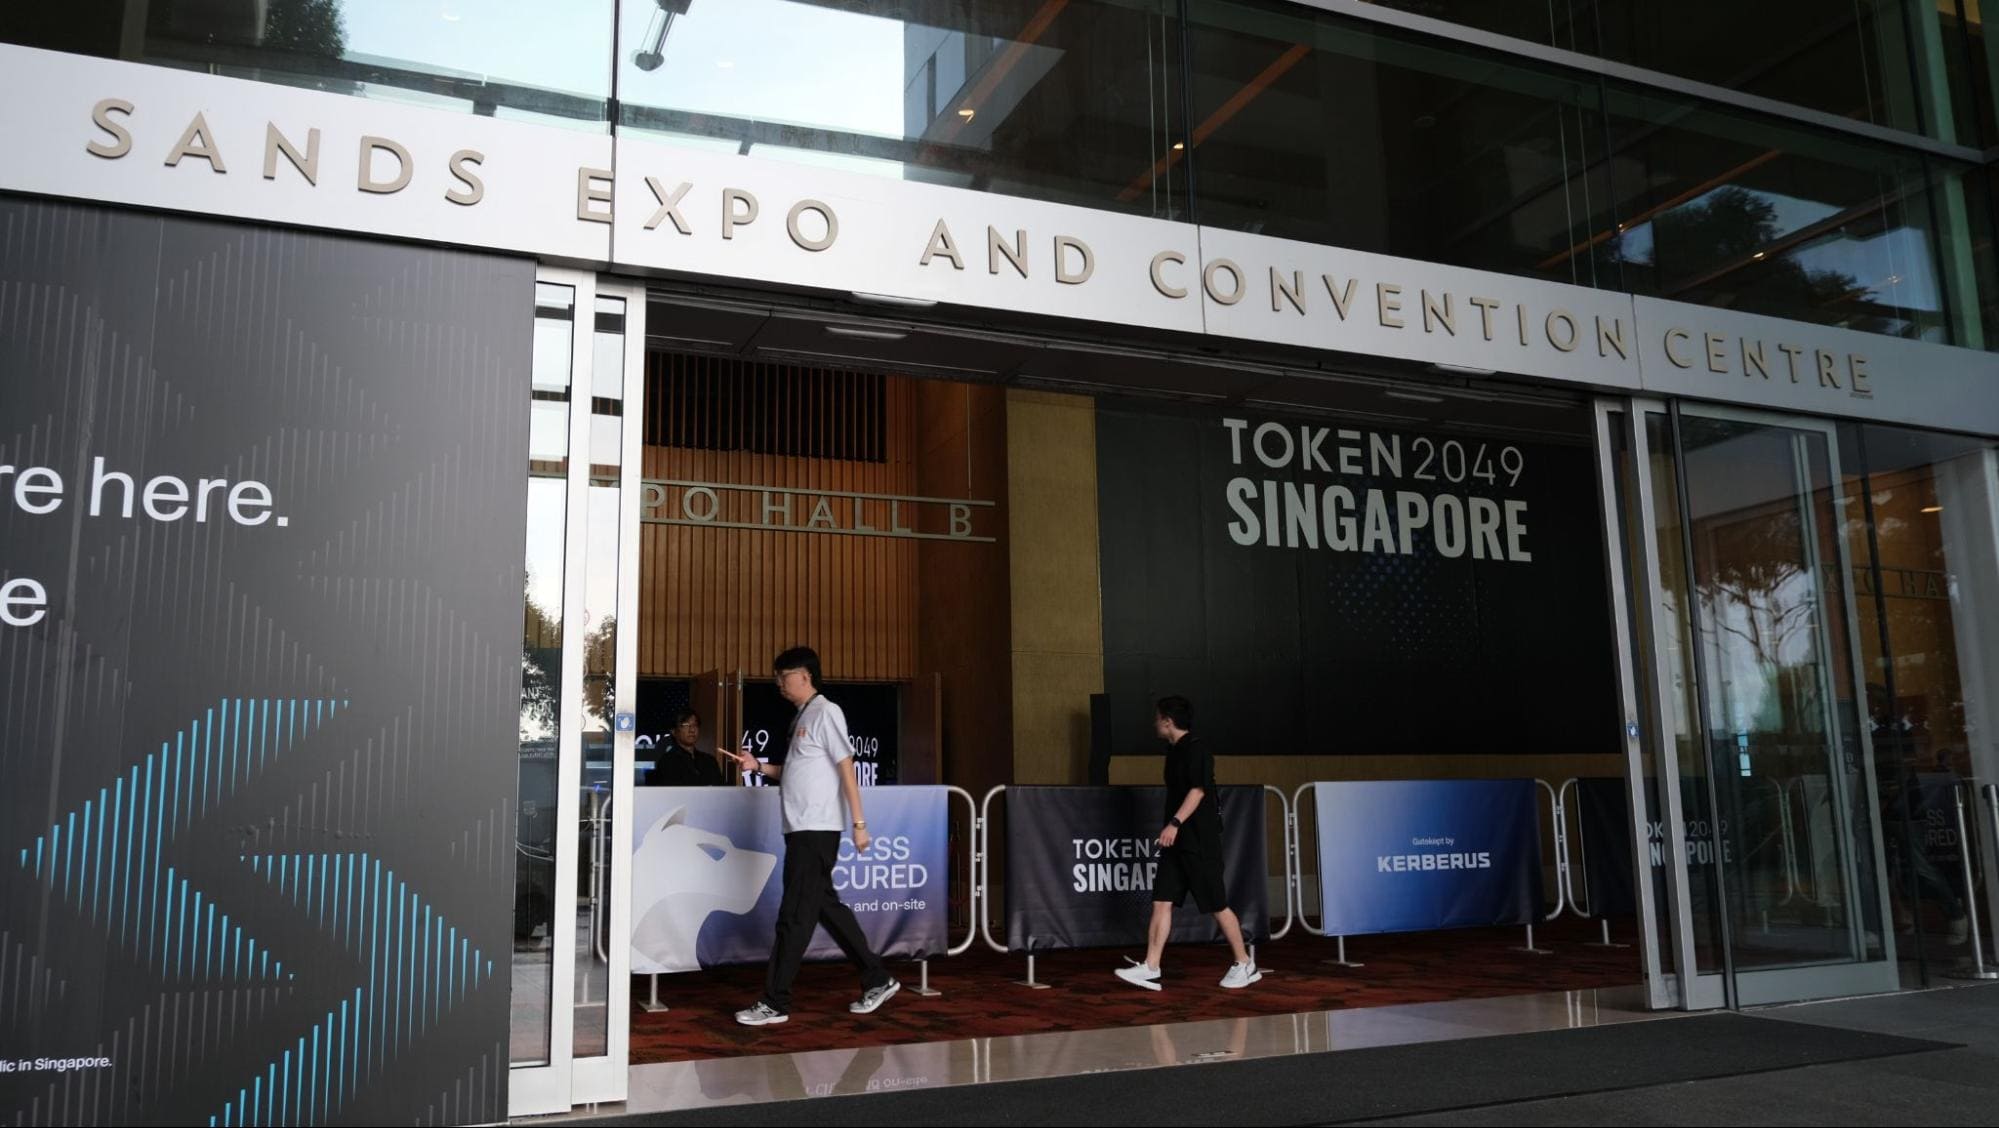
Q: What are your main goals for Token2049, in terms of engagement and showcasing Kerberus’ technology?
A: This is the first year we sponsored Token 2049 in Singapore. Our goal is for people to recognize that we are the security player on the block. We have been virtually underground since the beginning, but now we have made significant moves.
Last year, we acquired Fire, our top-three competitor. This year, we acquired Pocket Universe, our top competitor. We are essentially the player for B2C users in the crypto space, and we want everyone to know that.
The Bottom Line
Static defenses and after-the-fact reporting continue to leave crypto users exposed, while mainstream adoption hangs in the balance.
The next security benchmark must be real-time protection built into wallets and at the transaction level. Crypto won’t win trust by promising higher returns; it will win by proving users’ assets are safe in the first place.