The expansive Invicti (formerly Netsparker) alternative
Does Pentest-Tools.com cut itas an Invicti alternative?
Watch this 3 minute video and learn how to use the platform for penetration testing and vulnerability assessment.
I can highly recommend Pentest-Tools
The scope of tests provided is pervasive and covers a lot of potential system vulnerabilities. I was surprised by how many indicators are analyzed by (the) platform. I can highly recommend Pentest-Tools.
Pentest-Tools.com vs Invicti (formerly Netsparker)
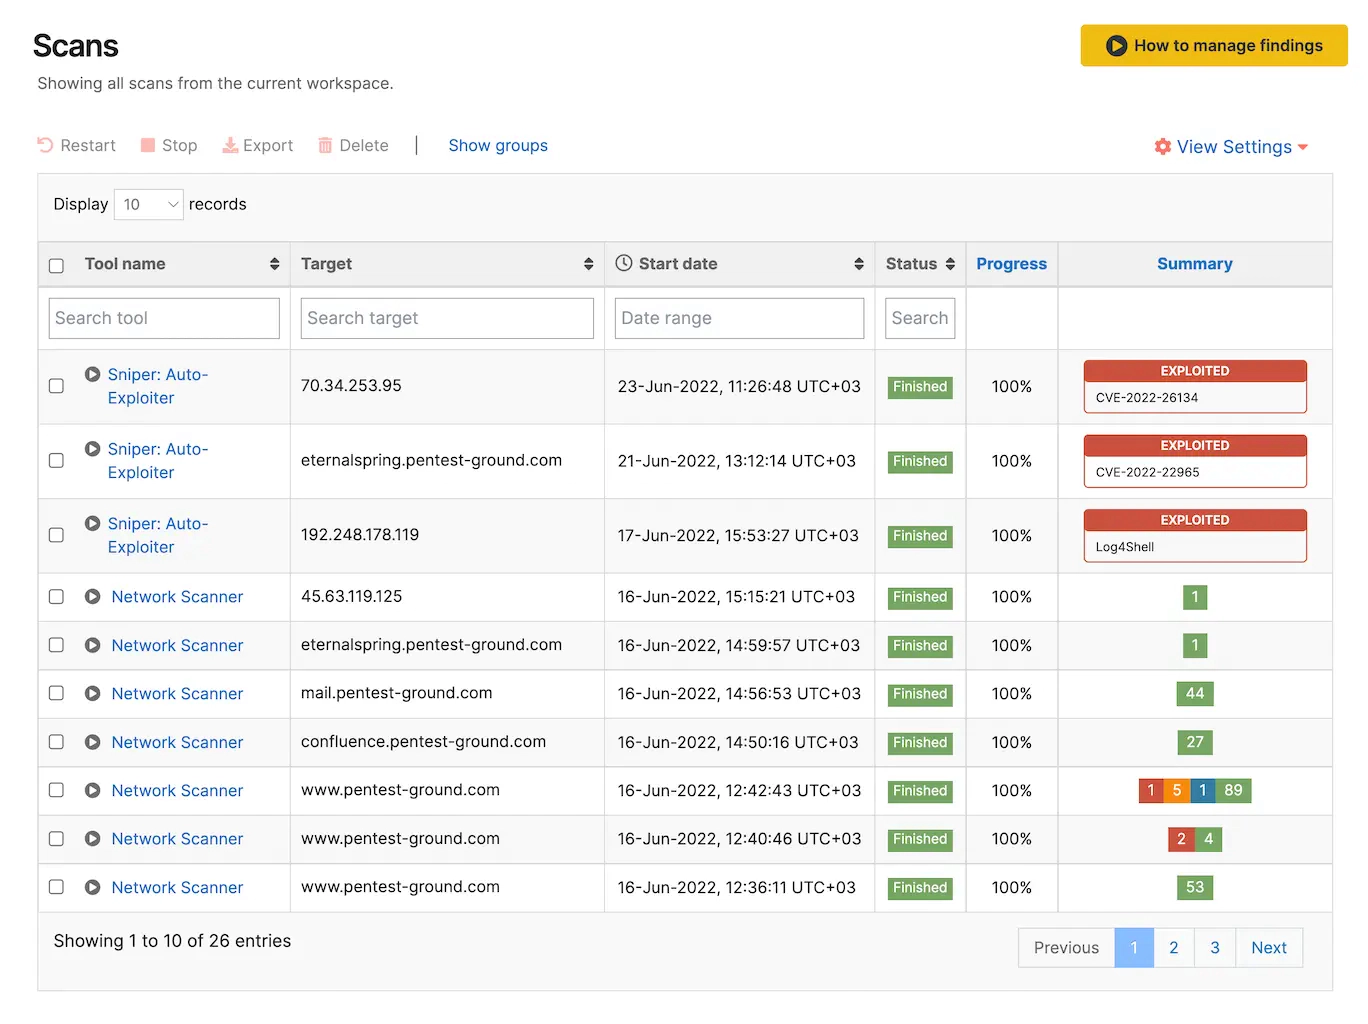
Are you working with SaaS clients as a security consultant or with security teams as an in-house pentester? Then you’ll be delighted with our chained detection and automatic exploitation tools, as well as our transparent and customizable reports for feeding back your findings. Pentest-Tools.com excels with its battery of aggressive vulnerability-seeking tools for online security professionals.
But, since you’ve landed on this page, you may be asking: How good is Pentest-Tools.com? How does it stand up in a side-by-side comparison with Invicti?
Explore the distinctives of each toolset so you can make an informed choice about your next pentesting investment.
Comparison
Pentest-Tools.com
vs
Invicti
Use cases
Designed to support the entire workflow of persistent penetration testers – from precision reconnaissance tools and focused CMS scanners to offensive tools and professionally designed, customisable report templates.
vs
Focused on the SDLC, meaning it’s geared to support development teams where a lack of substantial pentesting experience is skirted with pre-configured scan profiles, report policies and other built-in automation.
Range of available tools
Constantly updated range of 20+ flexible and interconnected security tools grouped in suites
Solutions for clients with web applications, CMSes, networks, and other types of non-web app targets: 7 reconnaissance tools; 3 types of scanners; and a host of offensive tools and utilities, including a new Sniper Auto Exploiter
vs
Chrome-based scanning engine primarily aimed at clients with web applications built using HTML 5 or Web 2.0; SPA Web apps and APIs
Crawling, scanning and reporting on the most common web application vulnerabilities such as SQL Injections, XSS and the OWASP Top 10 list
Specialized tools
Dedicated Content Management System scanners that can be deployed separately for rigorous and intelligent scanning of targets built on the top CMS software: WordPress, Drupal, Joomla and SharePoint
vs
Software Composition Analysis (SCA) sits alongside Dynamic Application Security Testing (DAST) and Interactive Application Security Testing (IAST) using agents that connect to web servers or application server engines to scan for open-source components and code
Connected tools
Linked and chained templates and tools that complement each other and help reduce repetitive tasks, such as automated vulnerability testing sequences; custom testing workflows; shared Items and Workspaces
vs
Desktop scanning software and Enterprise cloud scanner that is also available as an on-demand edition
Why security and IT pros prefer Pentest-Tools.com as an Invicti alternative
Pentest-Tools.com offers a comprehensive suite of tools that is hard to find in one product in the cybersecurity marketplace. We have over 20+ penetration testing tools that range from reconnaissance to vulnerability management all the way through to exploitation. Many experienced pentester reviews show their appreciation for this expansive tool stack that helps them tackle the depth and breadth of the critical security issues their clients face.
Our reconnaissance tools lead the offense, while our web vulnerability scanners identify the industry’s most common vulnerabilities. Meanwhile, CMS scanners tackle plugins, themes, and other components, while our network scanners plot the potential risks across the borders of your network. Finally, our aggressive (and controlled) offensive tools mimic the intent of even the most determined malicious raider.
Such a tool range has the capacity to cover everything from vulnerabilities in ASP.NET applications to all the usual exposed areas such as SQL injection and cross-site scripting; out-of-date versions, missing patches and misconfigurations. Everything is exploited, evidenced, and reported in real-time – with fewer false positives than other scanners. Our bang up to date vulnerability libraries, tools, and platform updates reinforce the rear, including scanning across web applications, CMSes and networks for the very latest attacks and business risks.
Pentest-Tools.com helped me scan my home servers to identify security concerns with my deployments. Their continued development and growth have been great to watch. Pen test tools gave me an idea of what issues or security vulnerabilities I was open to. They have an entire suite of tools to test my home environment. Some of my most used features were their website and network scanners, sniper: auto exploiter, various login page tests, and their subdomain finder to help me with subdomains I had forgotten about.
FAQs: Pentest-Tools as the Invicti (formerly Netsparker) alternative
So, is Pentest-Tools.com a better choice than the Invicti security scanner?
The answer is that it depends on what you want. It’s true that Invicti provides web application scanning. But, we assume you’ve landed on this page because you’re interested in researching technical pentesting solutions. If so, Pentest-Tools.com combines its proprietary and open-source tools to help you:
Launch intelligence-gathering recon missions
Establish scheduled vulnerability detection tours
Conduct bold, offensive activities
Make offense your best asset for strengthening defense.
Our customers rave about the sheer scope of tools from which they can select. You can deploy each independently for rapid identification, documentation and remediation of known weaknesses. But, you can also link and chain tools together for enhanced detection capability. And, if you work in a team environment, you can employ our cloud-based Shared Items and Workspaces to share your engagements, templates, robots, scans, findings, and reports.